Orosign
What Is Multi-Party Computation (MPC)? How It Works
October 23, 2026
10 mins read
Multi-party computation (MPC) lets several parties compute one result without revealing their inputs. See how MPC works, with examples and real uses.


Multi-Party Computation (MPC) is a cryptographic technique that lets several parties jointly compute a shared result without revealing their private inputs to one another. It solves a basic problem in distributed systems: how to work together on sensitive data without handing that data to a single operator. Today MPC runs in institutional wallets and custody, financial systems, healthcare analytics and cross-organization data collaboration, wherever privacy and shared control both matter.
MPC protects inputs while they are being computed on. Teams that also need evidence of how data was stored and processed pair it with Zero-Knowledge Proofs (ZKPs), cryptographic proofs that show a statement is true without revealing the data behind it. That is the layer Orochi Network works on with zkDatabase.
What Is Multi-Party Computation (MPC)?
Multi-Party Computation (MPC) allows multiple parties to jointly compute a function while keeping their individual inputs private. At no point does any single participant gain access to another party's raw data, even though the final result is computed correctly.
Formal definition vs intuitive explanation
Formally, multi-party computation, often called secure multi-party computation, is a class of cryptographic protocols that lets a group of participants evaluate a function over their combined inputs without revealing those inputs to one another. Each party learns only the final output and nothing else.
Intuitively, MPC is a way to "compute together without sharing." Each participant contributes encrypted or cryptographically split data, performs computations on those protected pieces and cooperates with the others to obtain a valid result, without exposing their private information.
Why MPC Is Foundational in Privacy-Preserving Cryptography
MPC addresses privacy at the computation layer, not just at storage or transmission. This makes it well suited to collaborative environments where trust between parties is limited.
Key reasons MPC is foundational:
- Protects sensitive data during computation, not only at rest or in transit
- Enables collaboration across organizations without data disclosure
- Removes the need for one intermediary to see every party's inputs
- Supports regulated and decentralized data-sharing environments
For a deeper look at the theory behind these guarantees, see our post on secure multi-party computation with information-theoretic techniques.
How Does Multi-Party Computation Work?
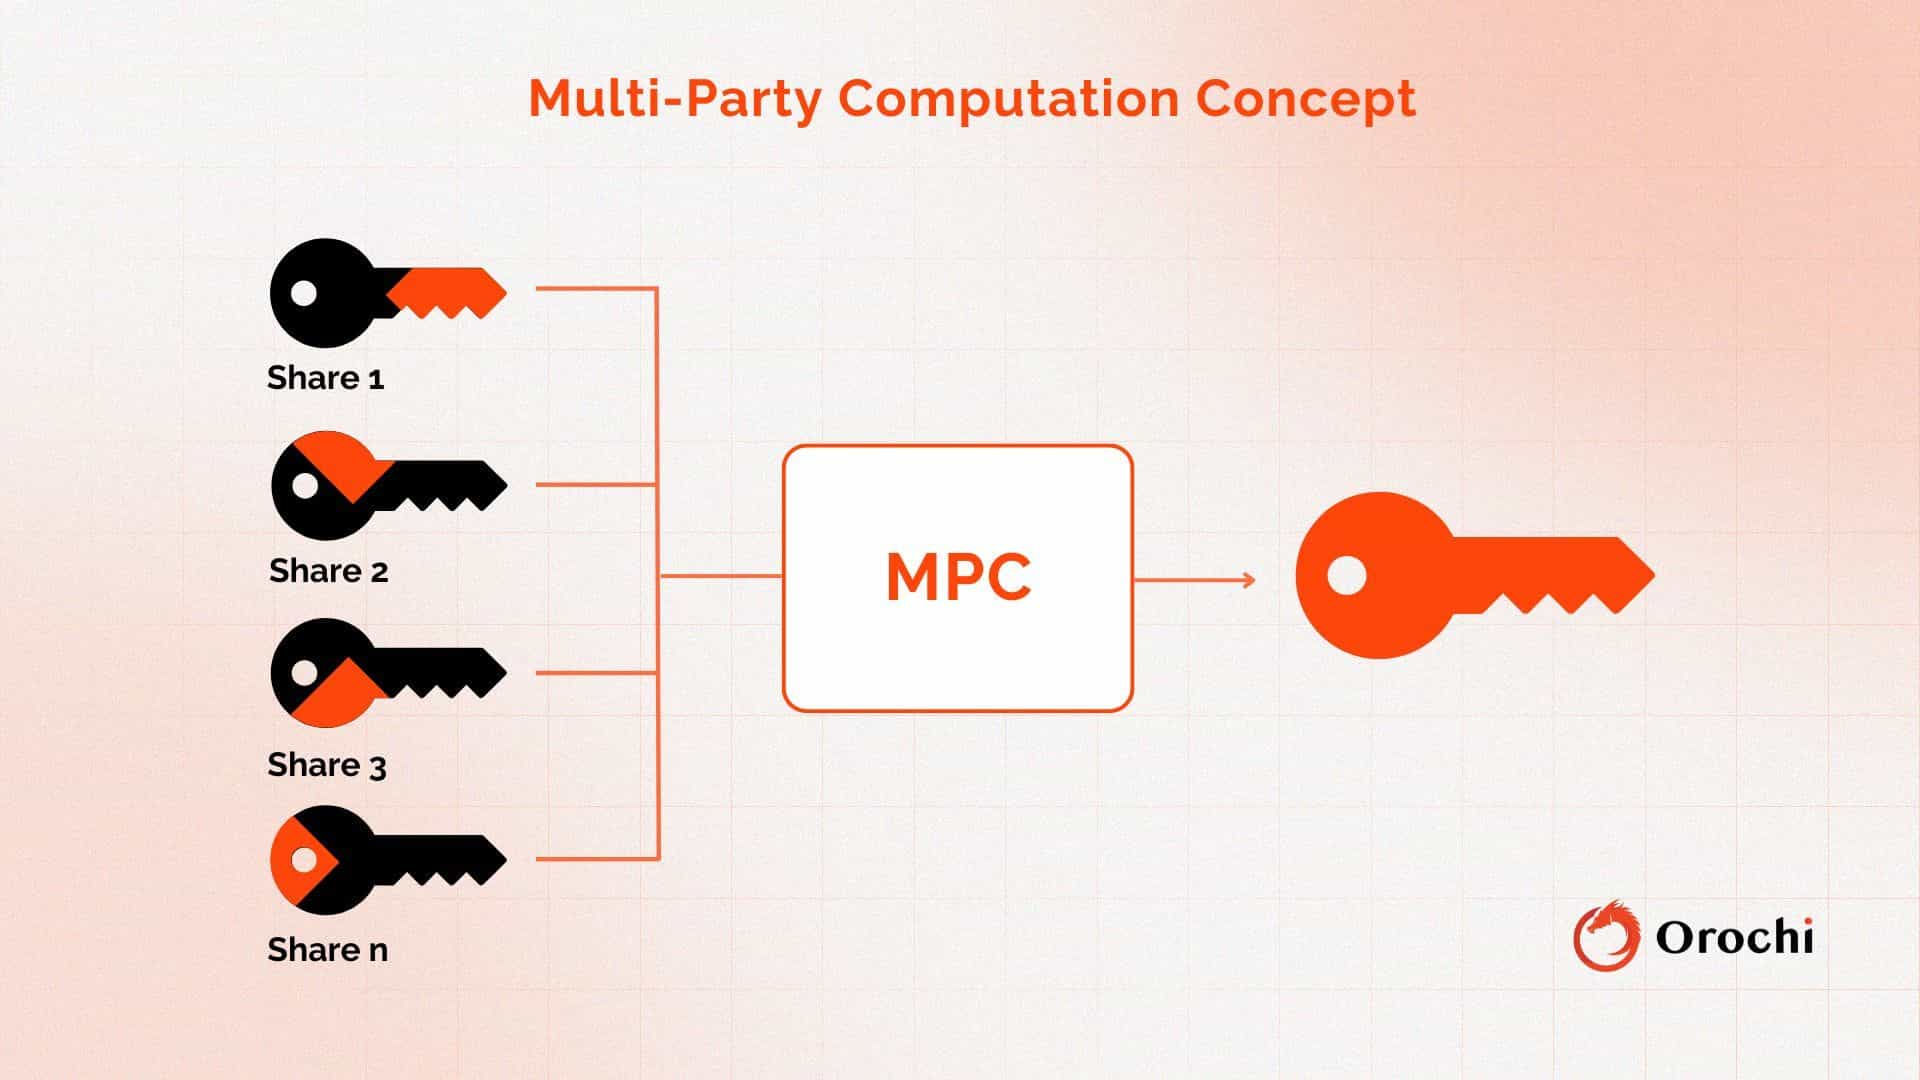
Multi-Party Computation (MPC) works by splitting private data into cryptographic shares and coordinating computation across multiple parties without reconstructing the original data in a single place. Computation runs on protected data fragments, so privacy is preserved from input to output.
Step 1: Input Secret Sharing
The first step in MPC is secret sharing, where each participant's private input is divided into multiple cryptographic shares. These shares are distributed across different parties or nodes in the system.
Individually, each share looks meaningless and reveals nothing about the original input, so one compromised participant does not expose the data.
Step 2: Distributed Computation
Once inputs are split into shares, computation is performed directly on those shares rather than on raw data. Each participant follows a predefined cryptographic protocol to process its share and exchange intermediate results with the others.
Private data is not revealed or reconstructed at this stage. The protocol keeps all intermediate values protected, so sensitive information stays hidden during processing.
Step 3: Result Reconstruction
After the distributed computation is complete, the final step is result reconstruction. The protected outputs from each party are combined to produce a single, correct result.
Only the final output is revealed. Individual inputs and intermediate computation states remain private to their owners throughout the workflow.
Core MPC Techniques You Should Know
Different MPC systems rely on different cryptographic building blocks depending on performance requirements, trust assumptions and threat models. Most practical MPC systems are built on a small set of core techniques that decide how data is protected and how computation is coordinated.
Secret Sharing Schemes
Secret sharing is the foundational technique behind most MPC protocols. Instead of storing or processing private data in one place, secret sharing splits a value into multiple cryptographic shares and distributes them across participants.
Two common approaches are:
- Shamir's Secret Sharing: A mathematical method that allows a secret to be reconstructed only when a minimum number of shares (a threshold) are combined. Fewer shares than the threshold reveal nothing.
- Additive Secret Sharing: A simpler approach where values are split into random parts that add up to the original secret. Each individual share is meaningless on its own.
In both cases the key idea is the same: no single party holds enough information to recover the original data.
Threshold Signatures and MPC Key Management
Threshold signatures apply MPC principles to key management and signing. Instead of one entity owning a private key, the key is distributed across multiple participants, each holding a share.
This approach is widely used in:
- Digital wallets to reduce single points of failure
- Institutional custody systems that require shared control
- Governance mechanisms where approvals must come from multiple parties
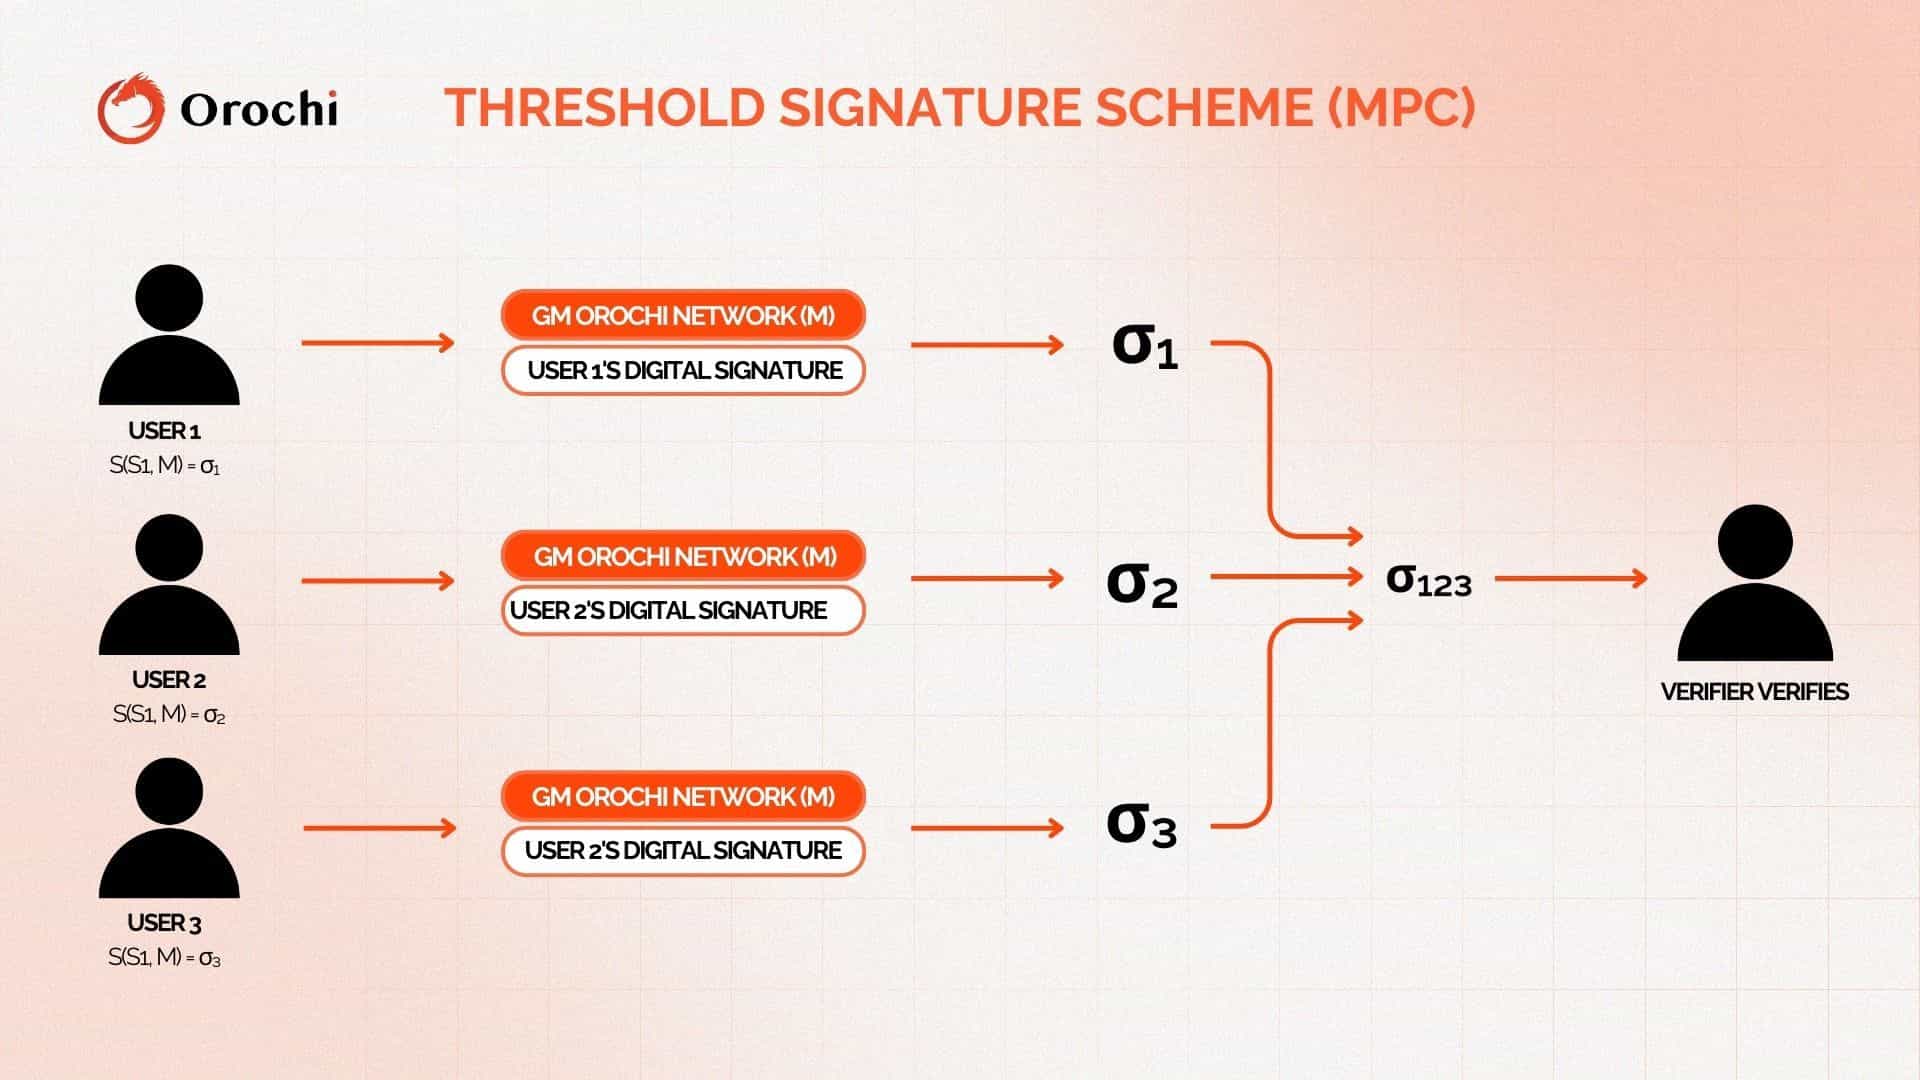
From the outside, a threshold signature looks like a normal cryptographic signature. Internally it is produced through coordinated computation among multiple key holders, without reconstructing the private key in one place.
MPC vs Homomorphic Encryption
MPC is often compared to Homomorphic Encryption (HE), another privacy-preserving technique. Both compute on protected data, but they differ in who does the computing.
- MPC: Distributes computation across multiple parties, each operating on secret shares. Privacy comes from collaboration and distributed trust.
- Homomorphic Encryption: Allows computation directly on encrypted data, typically by a single party holding the encrypted inputs. Our beginner's guide to fully homomorphic encryption covers how that works.
In practice, MPC is often preferred when:
- Multiple parties are already involved in the computation
- Trust needs to be minimized across organizations
- Key management and shared control are critical
- Flexibility matters more than single-operator execution
A Simple Example of Multi-Party Computation
Consider a familiar scenario: calculating an average salary across several companies.
Imagine several companies want to calculate the average salary across all their employees to benchmark pay. None of them is willing, or legally allowed, to share individual salary data with the others.
Using MPC, each company contributes its salary data in a protected form. The data is cryptographically split before it enters the computation. The companies then jointly compute the average without revealing individual salaries or internal payroll data.
At the end of the process:
- What is learned: the correct average salary
- What remains private: each company's individual salary data
No participant sees another company's inputs, and no central party ever holds the full dataset.
MPC is precise about what it exposes:
- It reveals only the final agreed result
- It does not reveal individual inputs
- It does not expose intermediate computation steps
- It does not require any party to hand over raw data
This strict separation between outcome and inputs is what makes MPC suitable for sensitive, regulated or competitive environments.
Why MPC is stronger than trusted third-party models
In a traditional trusted third-party model, every company would send its salary data to a central server or analytics provider. That creates a single point of trust and a single point of failure: if the central party is compromised, all the data is exposed.
Multi-party computation spreads that trust across participants instead. Even if one party is compromised, no single entity holds enough information to reconstruct the original inputs.
The Real-World Applications of MPC Today
Multi-Party Computation (MPC) already runs in production systems where privacy, integrity and shared control are critical. Across finance, healthcare, digital assets and enterprise data collaboration, organizations use it to work together without exposing sensitive information.
MPC in Financial Systems
In financial environments, MPC secures operations that need strict control and confidentiality.
- Secure transaction approval: Transactions can require multiple independent approvals without any single party holding full signing authority.
- Institutional custody: Private keys are distributed across multiple entities, reducing the risk of theft or insider compromise.
- Fraud detection: Institutions can jointly analyze transaction patterns and risk signals without sharing raw customer data.
MPC in Healthcare and Sensitive Data
Healthcare and research organizations often need to analyze data together while complying with strict privacy rules.
- Joint analytics without data leakage: Multiple parties can compute statistics across datasets without exposing patient data or proprietary information.
- Privacy-by-design collaboration: Sensitive information stays protected throughout the computation, even when datasets span different organizations.
MPC Wallets and Digital Asset Custody
Multi-Party Computation has become a core technology for digital asset wallets and custody. By distributing key shares across multiple parties, MPC wallets remove the single point of failure that a lone private key creates.
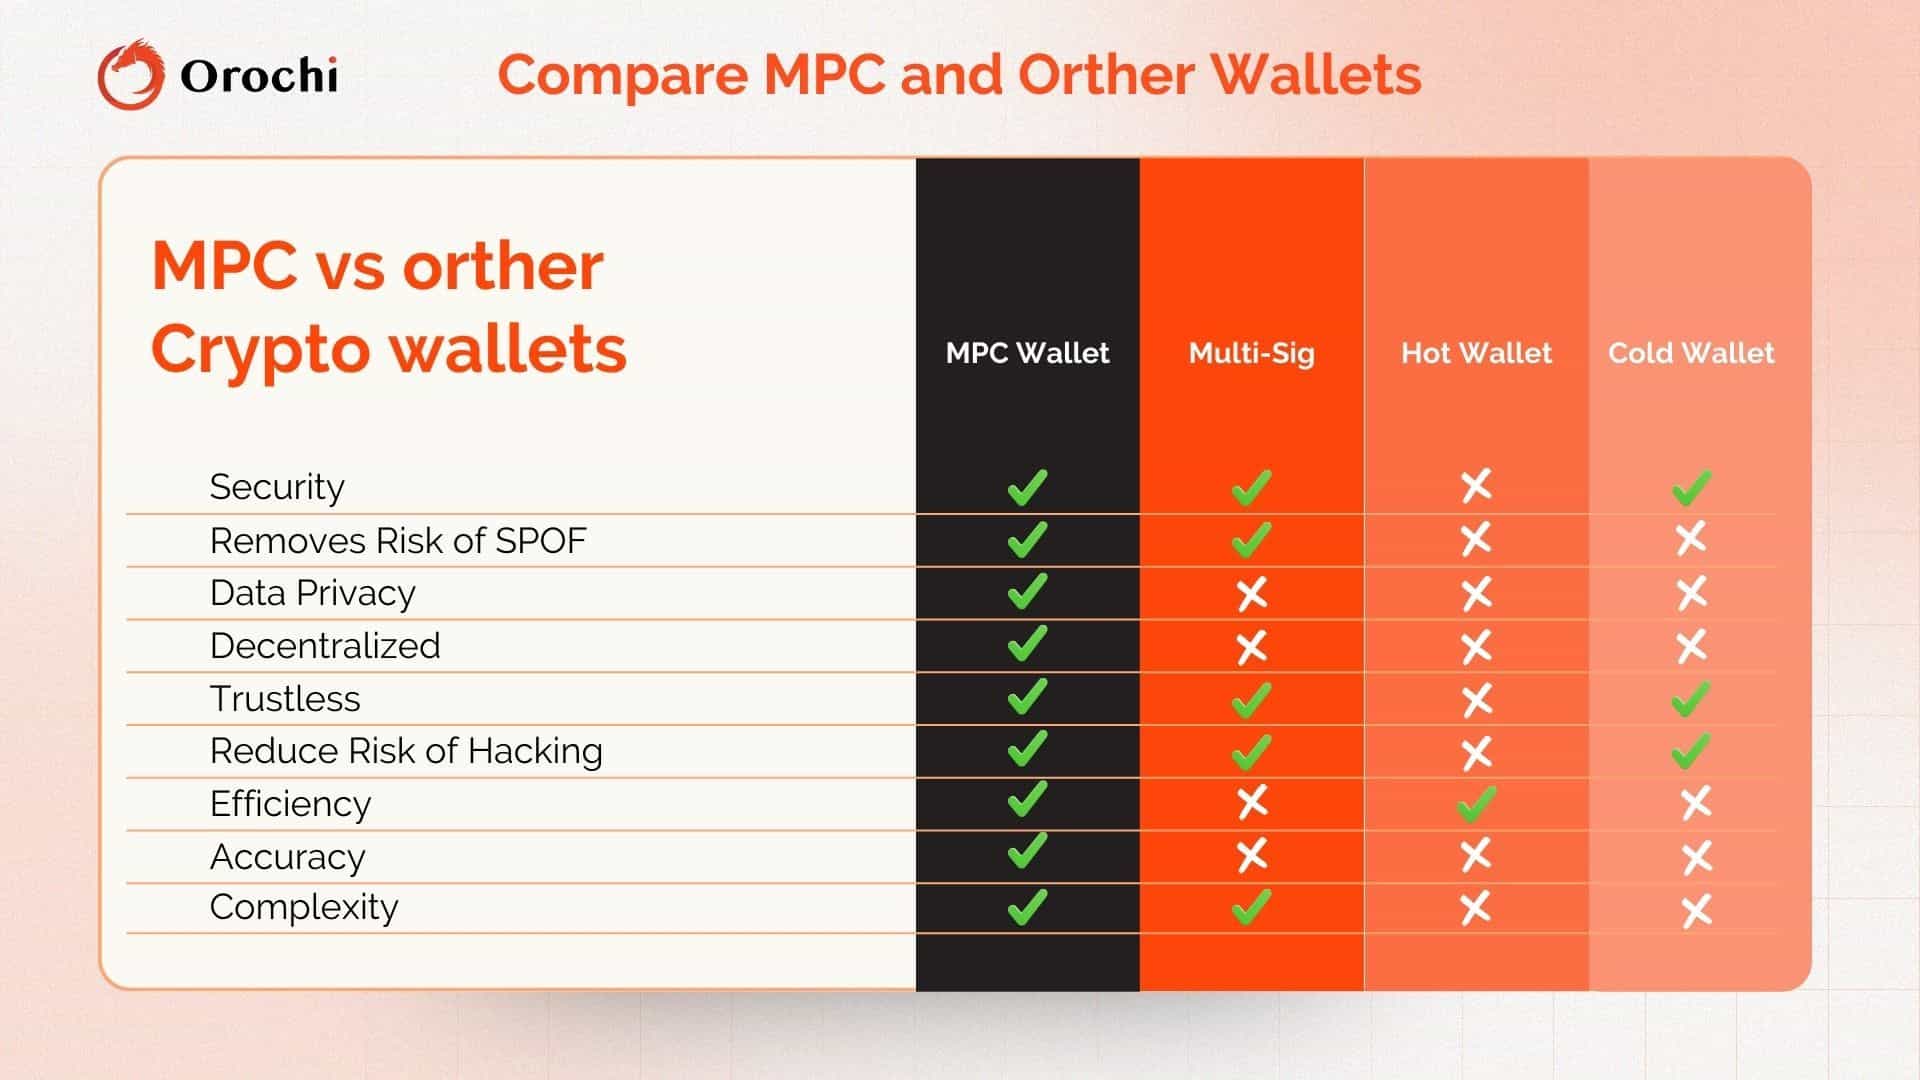
Unlike multisignature wallets, which require multiple on-chain signatures, MPC wallets generate a single standard signature through coordinated computation. This keeps transactions compact and compatible with any chain whose signature scheme the MPC protocol supports (for example ECDSA or EdDSA), while control stays shared. We compare the two models in detail in Multisig vs MPC: which is better for asset security.
Because the private key is never fully reconstructed, MPC wallets can also recover a lost key share and refresh shares without exposing key material.
Applying MPC with zkDatabase
MPC keeps inputs private while parties compute on them. It does not, by itself, give an outside party a proof of how the underlying data was stored, updated or queried. Auditors and counterparties who need that evidence look for a second layer.
zkDatabase is that layer: a verifiable database powered by Zero-Knowledge Proofs. It generates a proof for every update, query and transformation, so others can verify the data was stored and processed as claimed without seeing the raw data. It is the same idea behind privacy-preserving compliance, where a party proves a condition without exposing raw data. MPC protects the computation between parties, and zkDatabase proves what happened to the data. For the basics of the proofs involved, see what is a Zero-Knowledge Proof.
Conclusion
Multi-Party Computation (MPC) remains one of the most important techniques for privacy-preserving collaboration. It lets parties compute together without disclosing their data and keeps control shared where trust is limited. Systems that must also show auditors and counterparties how data was handled add a verifiable data layer next to it.
FAQs
What is Multi-Party Computation (MPC)?
Multi-Party Computation (MPC) is a cryptographic technique that allows multiple parties to jointly compute a result without revealing their individual inputs. Each participant learns only the final output, while all private data stays protected during the computation.
How is MPC different from multisignature (multisig) wallets?
Both MPC and multisig support shared control, but they work differently. Multisig wallets require multiple independent signatures to be submitted on-chain, while MPC wallets produce a single standard signature through coordinated computation off-chain.
Does MPC require a trusted third party?
No. In MPC, trust is distributed across participants, and no single party holds enough information to reconstruct private data or private keys, as long as fewer parties than the protocol's threshold collude.
Where is MPC commonly used today?
MPC is widely used in:
- Digital asset wallets and institutional custody
- Financial systems that require multi-party transaction approval
- Privacy-preserving analytics for sensitive data
- Cross-organization data collaboration in regulated environments
Explore zkDatabase: see how zkDatabase proves every update to your data without exposing it.
Related toOrosign