Verifiable Random Function & Oracle
Verifiable Random Function (VRF): How It Works in Blockchain
October 23, 2026
8 mins read
A verifiable random function (VRF) outputs a random value plus a proof anyone can check. See how VRFs work and how Algorand, Cardano and Polkadot use them.


A verifiable random function (VRF) is a cryptographic function that takes an input and a secret key and returns a pseudorandom output together with a proof. Anyone with the matching public key can use the proof to check that the output was computed correctly, but nobody without the secret key can predict or change it. That makes VRFs a widely used tool for randomness that must be fair and auditable on a blockchain: selecting block producers, running lotteries, assigning NFT traits and settling games.
What is a Verifiable Random Function (VRF)?
A verifiable random function is a type of cryptographic function that maps an input to a pseudorandom output and provides evidence that the output is authentic.
A VRF uses a public and private key pair (sometimes called a verification key and secret key) and an input, often called a seed. The VRF combines the private key and the seed to produce a random number and a proof. The proof makes the result verifiable while the secret key stays hidden, so the number remains unpredictable. Formally, given the input X, the holder of the secret key SK computes (Y, π) = F_SK(X), where Y is the pseudorandom output and π is the proof for Y. Anyone can check that Y was computed correctly using the proof π and the public key PK, but this information cannot be used to find the secret key SK.
RFC 9381, published in August 2023 by the IRTF's Crypto Forum Research Group (CFRG), describes a VRF as "the public key version of a keyed cryptographic hash": only the key holder can compute it, and anyone with the public key can verify it.
A verifiable random function has three core features, as its name suggests:
-
Verifiable: Anyone can check the validity of the output a VRF produces. They examine the proof with the public key and confirm the output matches. Only the owner of the secret key can compute the output, but anyone with the public key can verify it.
-
Random: To someone who does not know the secret key, the output of a VRF looks unpredictable and shows no pattern. RFC 9381 calls this property pseudorandomness.
-
Function: For a given key and input there is only one valid output. RFC 9381 calls this uniqueness: an adversary cannot produce two valid proofs that lead to different outputs for the same public key and input. This is what stops the key holder from trying many results and picking the one they like.
The history of VRF
The verifiable random function concept was first introduced by Silvio Micali, Michael Rabin and Salil Vadhan in 1999. Silvio Micali later founded the Algorand blockchain, whose consensus algorithm uses a VRF. The original construction was considered inefficient.
In 2005, Yevgeniy Dodis and Aleksandr Yampolskiy proposed a more efficient verifiable random function with shorter proofs and keys.
Later work by Dennis Hofheinz and Tibor Jager, and by Nir Bitansky, showed how to build VRFs from more standard cryptographic assumptions and general primitives rather than specific algebraic structures. These results are mainly theoretical; deployed VRFs, such as the ECVRF in RFC 9381, use efficient elliptic curve constructions.
Researchers have also proposed VRFs based on lattice cryptography, such as LB-VRF (Esgin et al., 2021), which is designed to withstand attacks from quantum computers, suggesting VRFs will stay relevant as cryptography moves to post-quantum assumptions.
In August 2023, RFC 9381 specified two practical constructions, RSA-FDH-VRF and the elliptic curve VRF (ECVRF), giving implementers a common reference. Our post on ECVRF explains the elliptic curve version in more detail.
Use Cases of VRF
Most random number generators do not produce numbers that can be cryptographically checked, so they are open to manipulation, which limits where they can be used. VRFs make the random value checkable, which opens up a number of use cases:
-
Internet security: VRFs help stop offline enumeration of hash-based data structures, for example in NSEC5, a proposal to prevent DNSSEC zone enumeration
-
Zero-knowledge technology: VRFs are used as building blocks in zero-knowledge protocols
-
Non-interactive lottery systems: VRFs let lotteries produce results that are efficient and fair
-
Verifiable transaction escrow schemes: VRFs support automated escrow services that preserve user anonymity
-
Blockchains and smart contracts: VRFs play a central role in decentralized protocols and applications
Application of VRF in Blockchain
VRFs are used in the consensus algorithms of several layer-1 proof of stake blockchains, where validators are chosen by their staked tokens rather than by mining. Algorand, Cardano and Polkadot use VRFs to randomly choose block producers.
Algorand
Silvio Micali, who co-created Verifiable Random Functions, is a well-known figure in computer science. He also founded the Algorand blockchain, which uses his invention to reach consensus.
Algorand has two kinds of nodes. Participation nodes hold stake and take part in proposing and voting on blocks. Relay nodes are network hubs that pass protocol messages quickly between participation nodes during block proposal and validation.
The VRF takes a secret key and a value and produces a pseudorandom output, with a proof that anyone can use to verify the result. The VRF functions similar to a lottery and is used to choose leaders to propose a block and committee members to vote on a block. This VRF output, when executed for an account, is used to sample from a binomial distribution to emulate a call for every algo in a user's account. The more algos in an account, the greater chance the account has of being selected -- it's as if every algo in an account participates in its own lottery. This method ensures that a user does not gain any advantage by creating multiple accounts. - according to Algorand Developer.
Micali used Verifiable Random Functions in Algorand to run cryptographic sortition, a private lottery that selects the block proposer and the validation committee. Using a VRF keeps the selection fair and unpredictable while keeping the consensus process light enough to scale. Other blockchain projects have since used VRFs to choose committees and block proposers.
Cardano
Cardano's Ouroboros proof of stake uses a VRF to let each node find out when it has earned the right to produce the next block. The inputs to the VRF are the slot ID (the current slot in the epoch), the node's VRF signing key and an epoch nonce built from earlier blocks. An epoch is a fixed period made up of many slots, and each slot is a short window in which one block can be produced.
Shortly before each slot, every node uses the VRF to produce a random value that answers the question "do I have the right to create a block in this slot?". Nobody can predict in advance which node will win the right to produce the next block.
Polkadot
Polkadot uses verifiable random functions very close to those in Ouroboros. The difference is that the VRF used in Polkadot's BABE consensus does not rely on a central clock. Instead it relies on earlier outcomes, and it approximates time using slot numbers as a simulated clock.
_Validators participate in a lottery in every slot (currently 6 seconds) which will tell them whether they are a block producer candidate. This lottery is based on VRF (Verifiable Random Function) which validators use to compute a random number. This function is also used to prove that the number validator provided was truly valid and it's thus eligible for a lottery. The validator wins the lottery if v < T where v is the validators random number and T is generated number by the network. After the lottery, several scenarios actually come into play - one validator wins, multiple validators win, and finally a situation where there is no block producer candidate. - According to _Polkadotters
Elsewhere in the blockchain ecosystem
Smart contract developers also need a source of randomness for their applications. Blockchains are deterministic, so on-chain apps have no built-in secure random number generator. Using block hashes as a random source invites manipulation by miners or validators, who can withhold blocks with unfavorable hashes. Simple off-chain solutions are opaque and give no evidence that the random value was not altered by the oracle node or the data source.
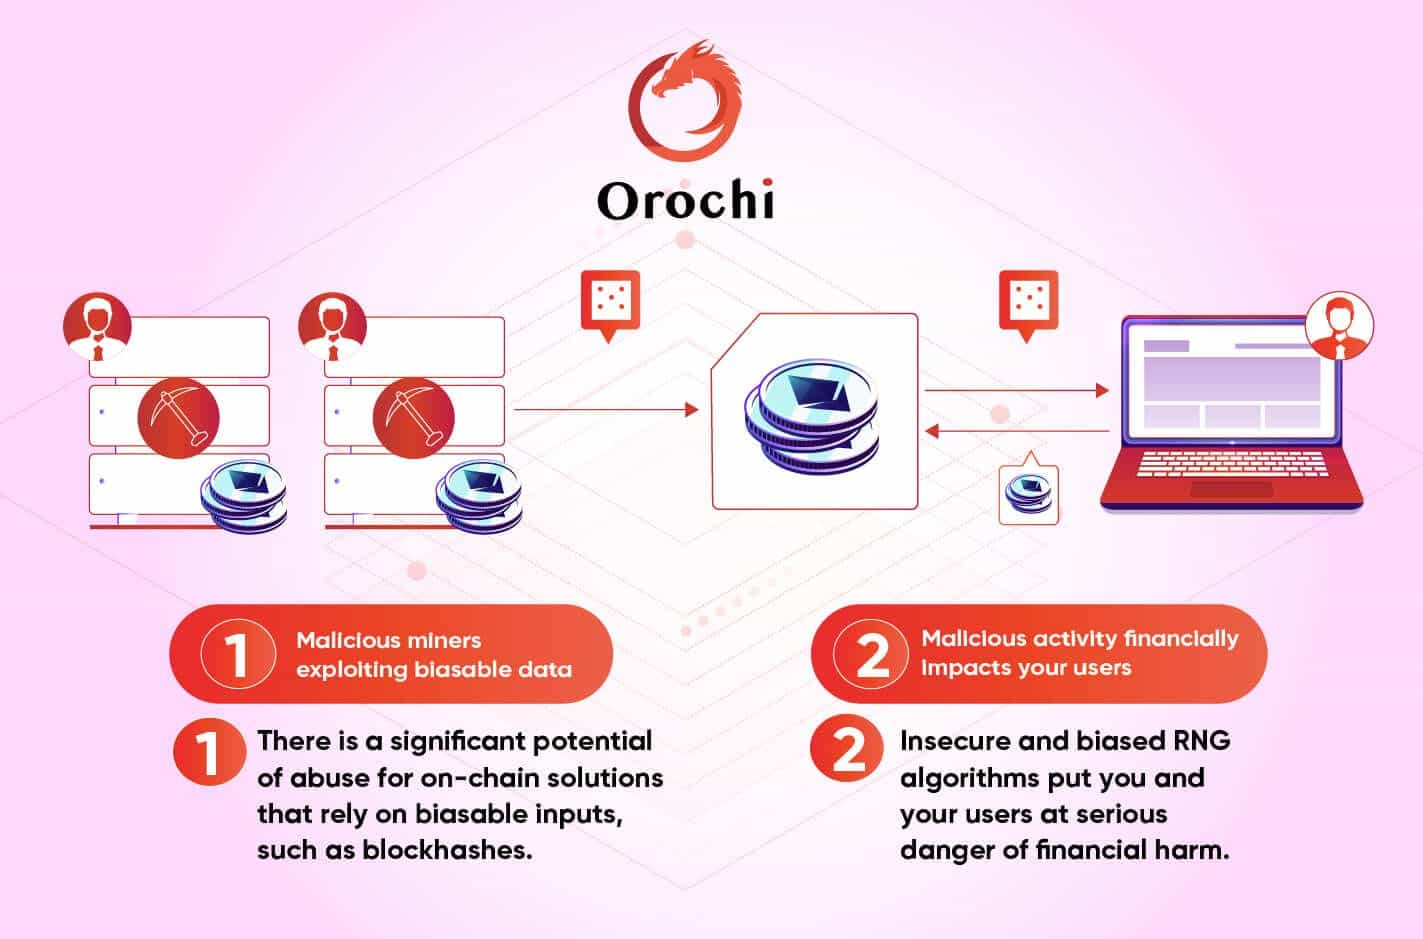
A well-designed system that relies on randomness should be provably fair and give every participant the same uncertainty. That also lowers the chance that an attacker can exploit a contract by predicting its outcome. For a wider look at why this matters, see the importance of randomness to blockchains and Web3.
Using a VRF in smart contracts
A smart contract that uses a VRF can show every user that its random result came from the agreed input and key and was not changed afterward. A game, lottery or NFT mint gets a random value together with a proof that the contract checks before using it.
Proof of stake blockchains rely on the same property to choose validators fairly. If that selection could be biased, an attacker could tilt block production in their favor, which weakens decentralization. A VRF closes that gap because every selection comes with a proof that anyone can check. Orand, the VRF service from Orochi Network, delivers that kind of verifiable randomness to smart contracts on chains compatible with the Ethereum Virtual Machine (EVM). Introducing Orand explains how it works, and our list of the top implementations of verifiable random functions compares other options.
View Docs: see how to request verifiable randomness from Orand in your smart contract.
Related toVerifiable Random Function & Oracle