



How Oracle Manipulation Happens in Prediction Markets: The Polymarket $7M Case
July 4, 2026
4 mins read
In March 2025, a single actor used 25% of UMA voting power to falsely settle a $7M Polymarket contract. This is how it happened, why oracle systems are vulnerable to governance attacks, and what verifiable data infrastructure can do about it.


In March 2025, a single actor controlling 25% of UMA voting power falsely settled a $7 million Polymarket contract on Ukraine's mineral deal. The attack exposed structural weaknesses in oracle-dependent prediction markets — and raised a harder question: can oracle integrity ever be guaranteed without cryptographic proof?
What Happened on Polymarket
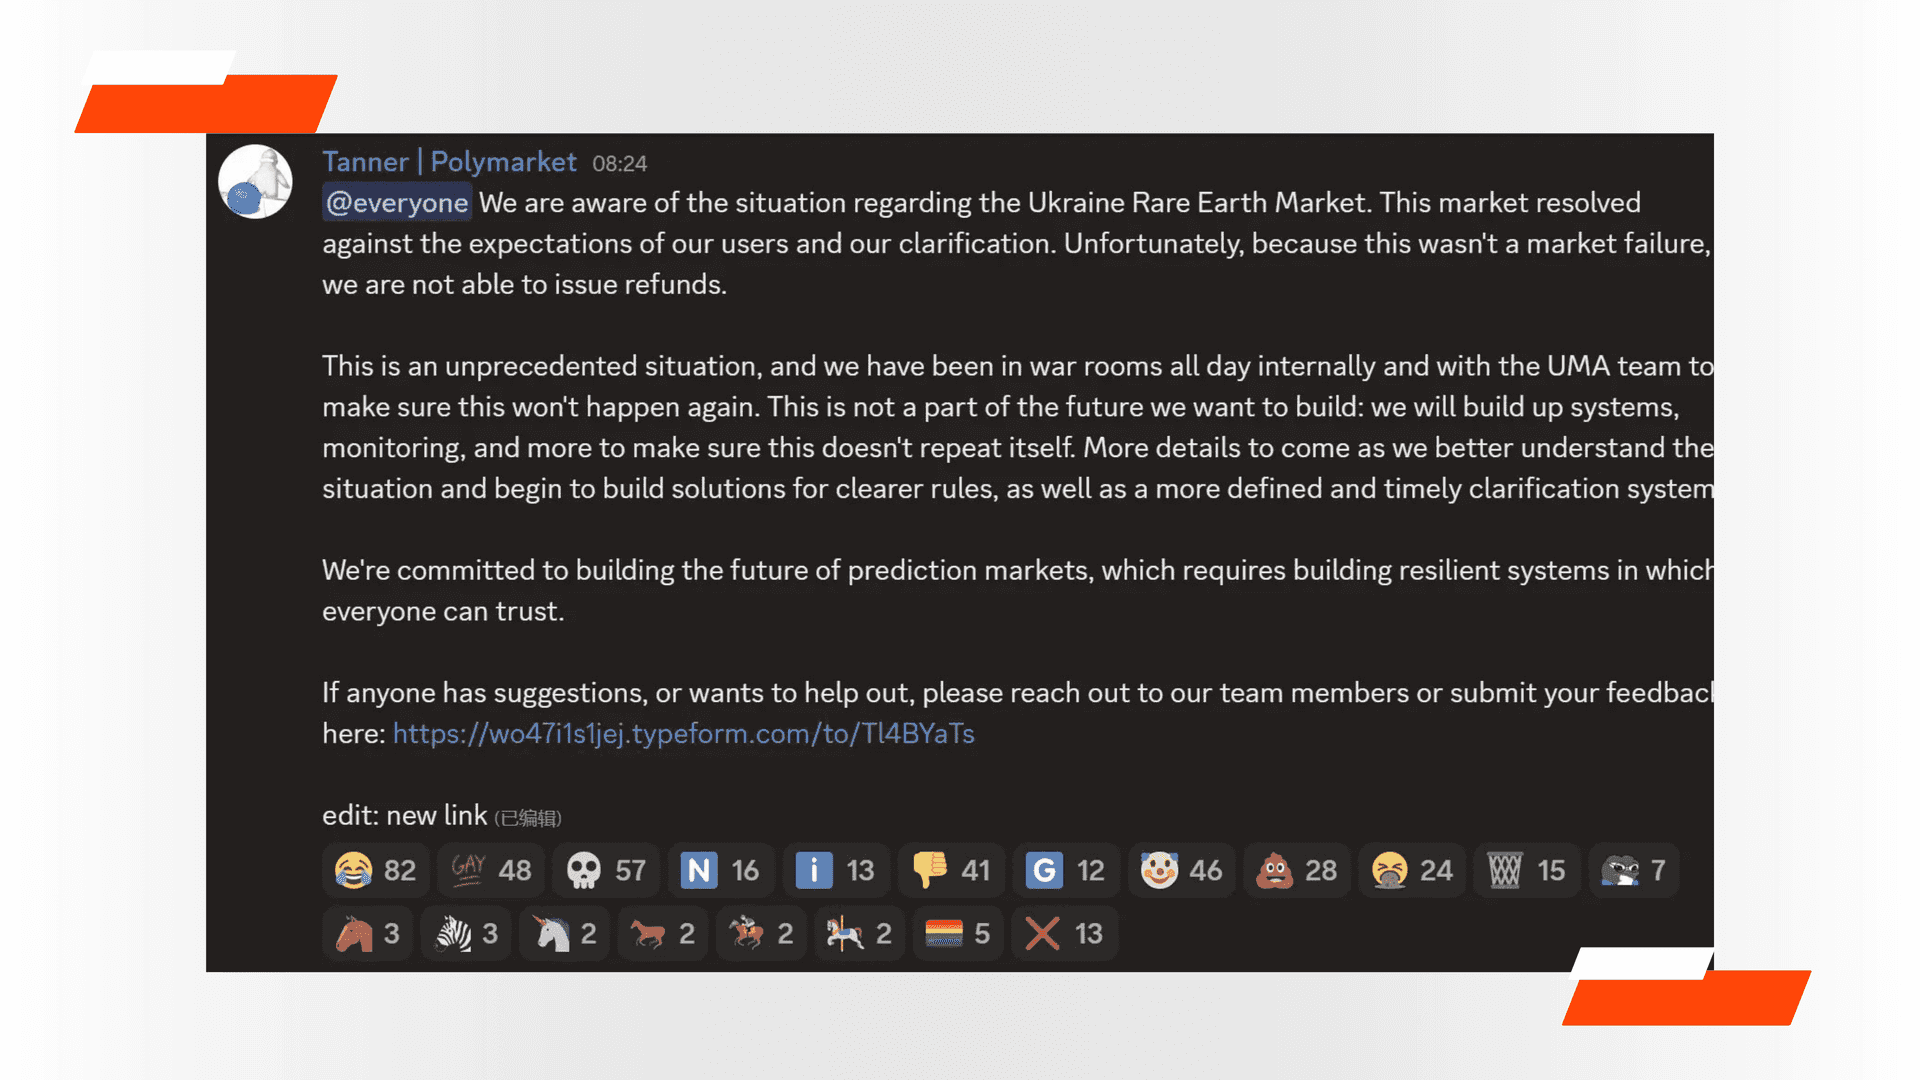
Between March 24 and 25, 2025, a governance attack targeted Polymarket's contract "Will Ukraine agree to Trump's mineral deal before April?" The contract's odds moved from 9% to 100% and resolved as "Yes" — despite no official agreement being reached.
The attacker, a large UMA token holder, cast 5 million UMA tokens across three accounts, representing 25% of total votes in the dispute resolution round. Polymarket's resolution mechanism allows any proposer to stake 750 USDC.e to submit an outcome. If disputed, UMA token holders vote to settle. Concentrated voting power bypassed this check entirely.
The result: $7 million paid out on a false resolution.
Why Oracle Systems Are Vulnerable to This
The Polymarket attack is one instance of a broader structural problem, part of a pattern of oracle and verification failures recorded across DeFi and RWA. Oracle systems, regardless of design share several recurring failure points.
Governance Concentration
When token-weighted voting determines outcomes, large holders can override smaller participants. Decentralization in name does not mean decentralization in practice. The UMA incident showed that 25% stake is sufficient to control a dispute round when other participants are passive or absent.
Centralization as a Single Point of Failure
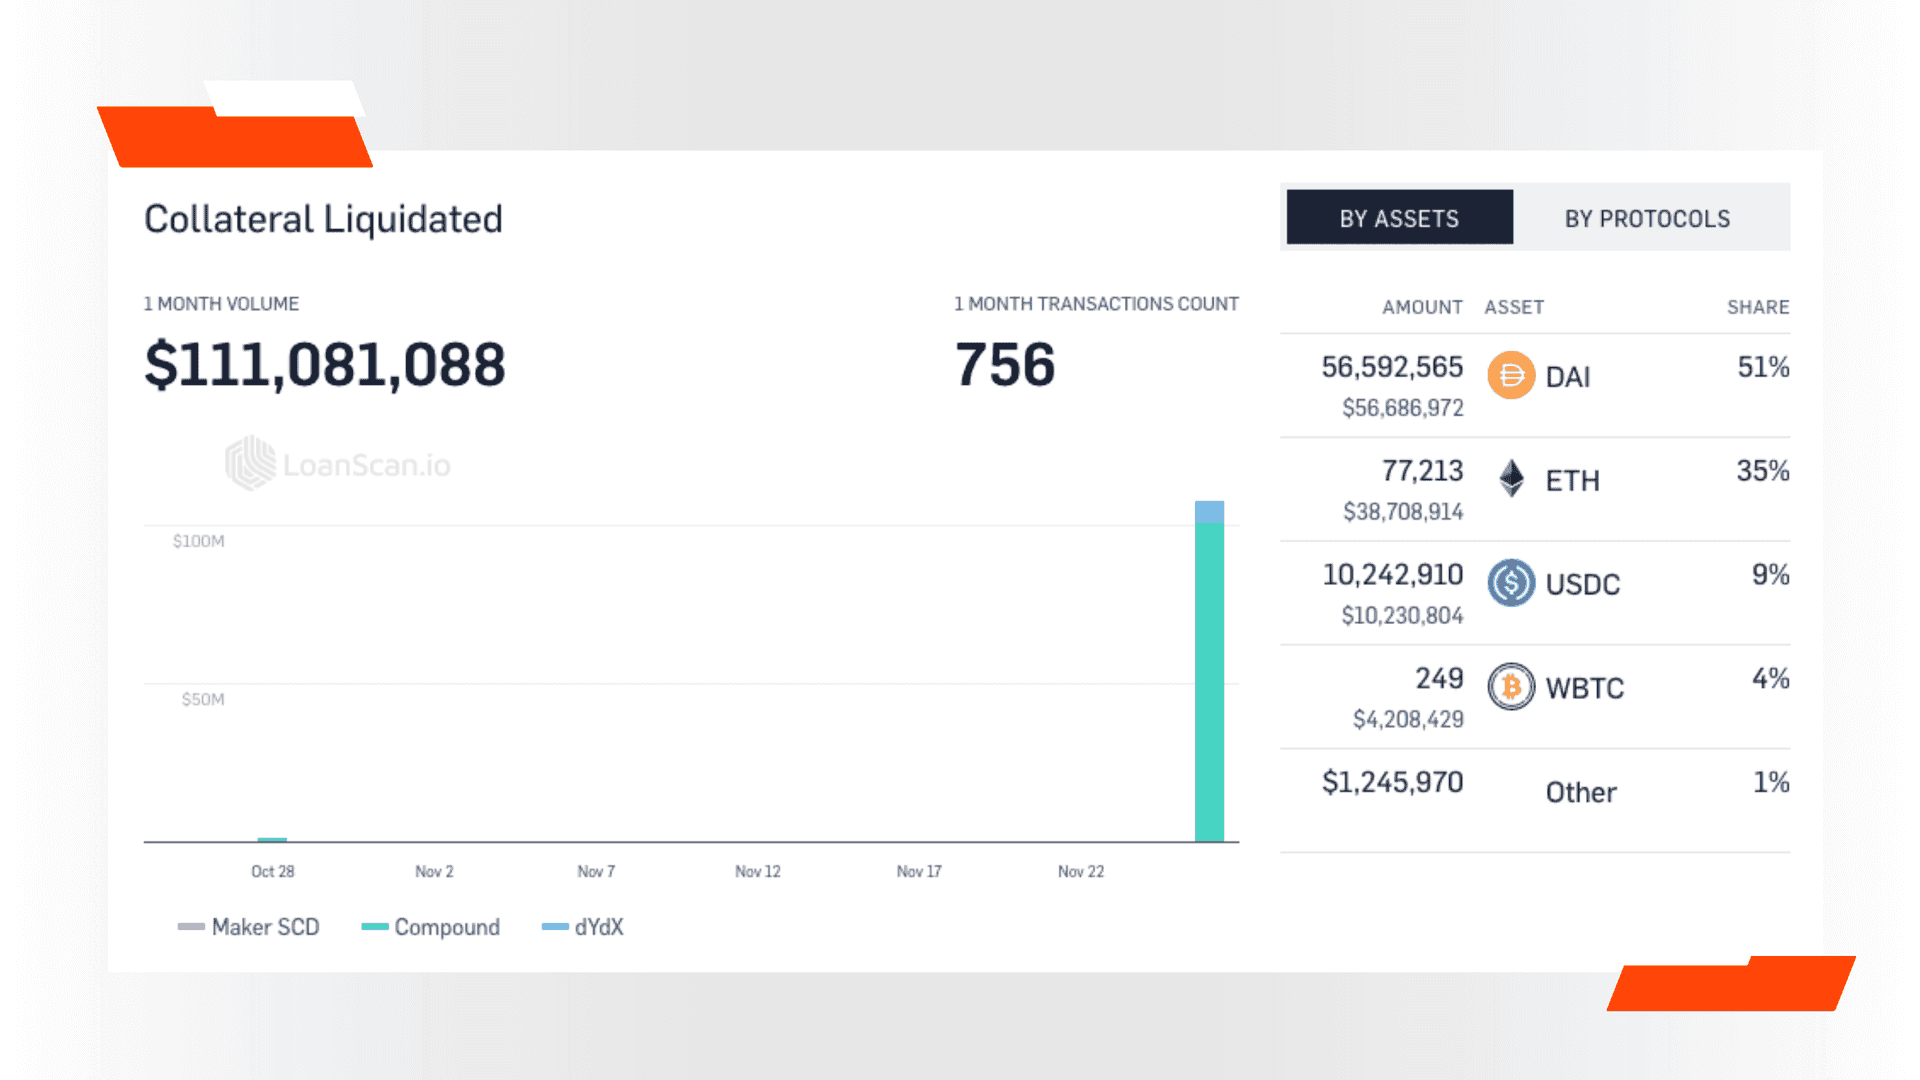
Centralized oracles introduce a single point of failure at the data feed level. In November 2020, Compound experienced an $89 million liquidation event after a CoinbasePro oracle reported DAI at $1.30 instead of ~$1.00. The wrong price triggered automated liquidations across the protocol before the error was corrected. The root cause: a single data source with no cryptographic verification of the reported value.
Scalability Under Load
High transaction volumes create latency in oracle data delivery. When data arrives late or out of sequence, smart contracts execute on stale prices. This is not a theoretical risk — it is a recurring issue in DeFi protocols during periods of high market volatility, when accurate pricing matters most.
The Verification Gap
The deepest problem is not governance design or latency — it is the absence of cryptographic proof at the data layer. Oracle systems deliver data. They do not prove that the data is correct, that it was not modified in transit, or that the computation producing it followed the stated rules. Trust is assumed, not verified.
Orochi Network's Approach: Verifiable Data at the Source
Orochi Network addresses the verification gap through two components of its Verifiable Data Infrastructure stack.
zkDatabase is a noSQL database built on a Merkle DAG-based distributed storage system. Every operation — ingesting data, querying records, updating entries, modifying schema — generates a Zero-Knowledge Proof. That proof can be verified by any external party: a smart contract, a regulator, a counterparty. No trust in the database operator is required. In the context of prediction markets, this means the data feeding a contract resolution can carry a cryptographic proof of its integrity before any vote is cast.
Applied to the Polymarket Case
Had Polymarket's resolution mechanism required cryptographic proof of the underlying event — not just a staked assertion — the UMA tycoon's vote would have been irrelevant. The data would have either proven the mineral deal occurred, or it would not have. No amount of voting power changes the output of a Zero-Knowledge Proof.
The $7 million loss was not a failure of tokenomics design. It was a failure of the verification layer.
Closing Note
The Polymarket governance attack is a precise example of what happens when trust replaces proof in high-stakes financial systems. As on-chain prediction markets, RWA protocols, and institutional DeFi grow in scale, the cost of that assumption rises. Verifiable data infrastructure — where every state transition carries a cryptographic proof — is not a future upgrade. It is the missing foundation.
Risk Disclaimer: This article is purely objective and for illustrative purposes only, with absolutely no intent of opposition or challenge in any form.
Reading more Orochi's Insiders below:
Related to




